Information Security Policy
(1) Policy Statement
We uphold the information security management principles of ISO/IEC 27001 and are committed to “establishing information security systems, improving the information security environment, developing information security capabilities, and achieving information security objectives.” We ensure that all personal data and information assets maintain confidentiality, integrity, and availability throughout transmission, storage, and processing, thereby safeguarding the interests of our customers, business partners, and the Company.
(2) Scope of Application
This policy applies to:
- Personnel:All employees, contractors, and visitors.
- Systems & Facilities:All company information systems, equipment, and cloud services (including server room management).
- Confidential Information:Sensitive data, drawings, and test reports involved in collaboration with aerospace customers.
- Core Business:Information security operations management in the production process of airplane landing gear and shock absorber modules.
(3) Three Core Principles of Information Security
- Confidentiality:Ensuring that only authorized personnel can access confidential information and customer data, preventing unauthorized access.
- Integrity:Preventing unauthorized modification of data and ensuring the accuracy and correctness of design and test information.
- Availability:Ensuring that critical systems and information are accessible and usable by authorized users when needed.
(4) Organization and Responsibilities
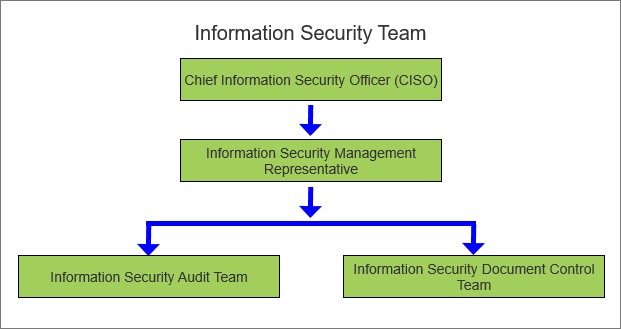
We have established a comprehensive information security governance framework led by the Chief Information Security Officer (CISO), who oversees information security management and the implementation of security policies. A dedicated information security team and Information Security Control Team are responsible for risk management, policy development, and security controls, ensuring the effective operation of the Information Security Management System (ISMS).
All departments participate in information security management according to their responsibilities. Through cross-functional collaboration, we integrate information security requirements into our operations and continuously enhance overall information security management effectiveness.
(5) Continual Improvement
We are committed to information security and data protection. Under the leadership of the Chief Information Security Officer (CISO), we have established an information security governance framework supported by a dedicated team responsible for risk management, policy development, and implementation, continuously strengthening our security capabilities.
To safeguard the confidentiality, integrity, and availability of information assets, we regularly conduct risk assessments, audits, and related management activities, while continuously enhancing the security controls of our networks, systems, and equipment to ensure the effective operation of our Information Security Management System (ISMS).
In addition, we actively promote information security awareness and training programs to enhance employees’ security awareness and integrate security principles into daily operations and corporate culture. Through these efforts, we strive to provide a secure, reliable, and trustworthy environment for our stakeholders.